Resources
BHIS Blog
Current cybersecurity commentary and technical guidance.
Intercept Lab
Lab 1 - The Intercept Scenario : Your team is hired to test the downlink resilience of a startup's CubeSat, ODYSSEY-1 They claim the link is secure. You're given two historical baseband captures from…
Defending Odyssey Lab - Part 1
Blue Lab 1 - Defending ODYSSEY-1: API & DoS Protection Scenario: You are blue team for ODYSSEY-1. Red team has: Replayed stale telemetry into the groundstation Flooded and on your groundstation…
zeek
Zeek — SOC Analyst Playbook (Cheat-sheet + Expanded) Zeek (formerly Bro) is an event-driven network security engine that passively monitors traffic, parses protocols, extracts metadata and generates…

wireshark
Wireshark Wireshark is a powerful open-source network protocol analyzer used for capturing and analyzing packets in real time. It is an essential tool for any SOC Analyst to inspect suspicious network…
WinEventViewer
Windows Event Viewer Windows VM The file for the lab is under: Windows Event Viewer is a built-in administrative tool that allows users to view and analyze logs of system, security, and application…
tcpdump
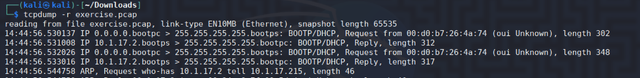
tcpdump tcpdump is a powerful command-line packet analyzer that allows you to capture and inspect live traffic on a network. It is commonly used for quick triage, scripting, and environments where a…
suricata
Suricata Suricata is a powerful open-source Network Security Monitoring (NSM), Intrusion Detection System (IDS), and Intrusion Prevention System (IPS) engine. Developed by the Open Information…
snort
Snort Snort is an open-source Network Intrusion Detection System (NIDS) and Intrusion Prevention System (IPS) developed by Cisco. It inspects network traffic in real-time and uses a powerful…
PEStudio
PEstudio for Linux Overview PEstudio is a static analysis tool used to examine Windows executables for potential indicators of compromise without running the file. While PEstudio is natively a Windows…
IDA Free
Overview IDA Pro (Interactive DisAssembler) is a powerful disassembler and debugger used in malware analysis, reverse engineering, and vulnerability research It converts binary executables into…
Hayabusa
Being the first time you have probably heard about this tool, if you search it up you will get some japanese motorcycles, search Hayabusa event viewer. Hayabusa-Repo Setup Using the actual tool Some…
FTK Imager
FTK Imager Documentation Overview FTK Imager is a free forensic tool from AccessData used to preview and capture data in a forensically sound manner. In SOC and IR work, it’s mainly used to acquire…